Detection Engineer
Threat report in. Tested detection out.
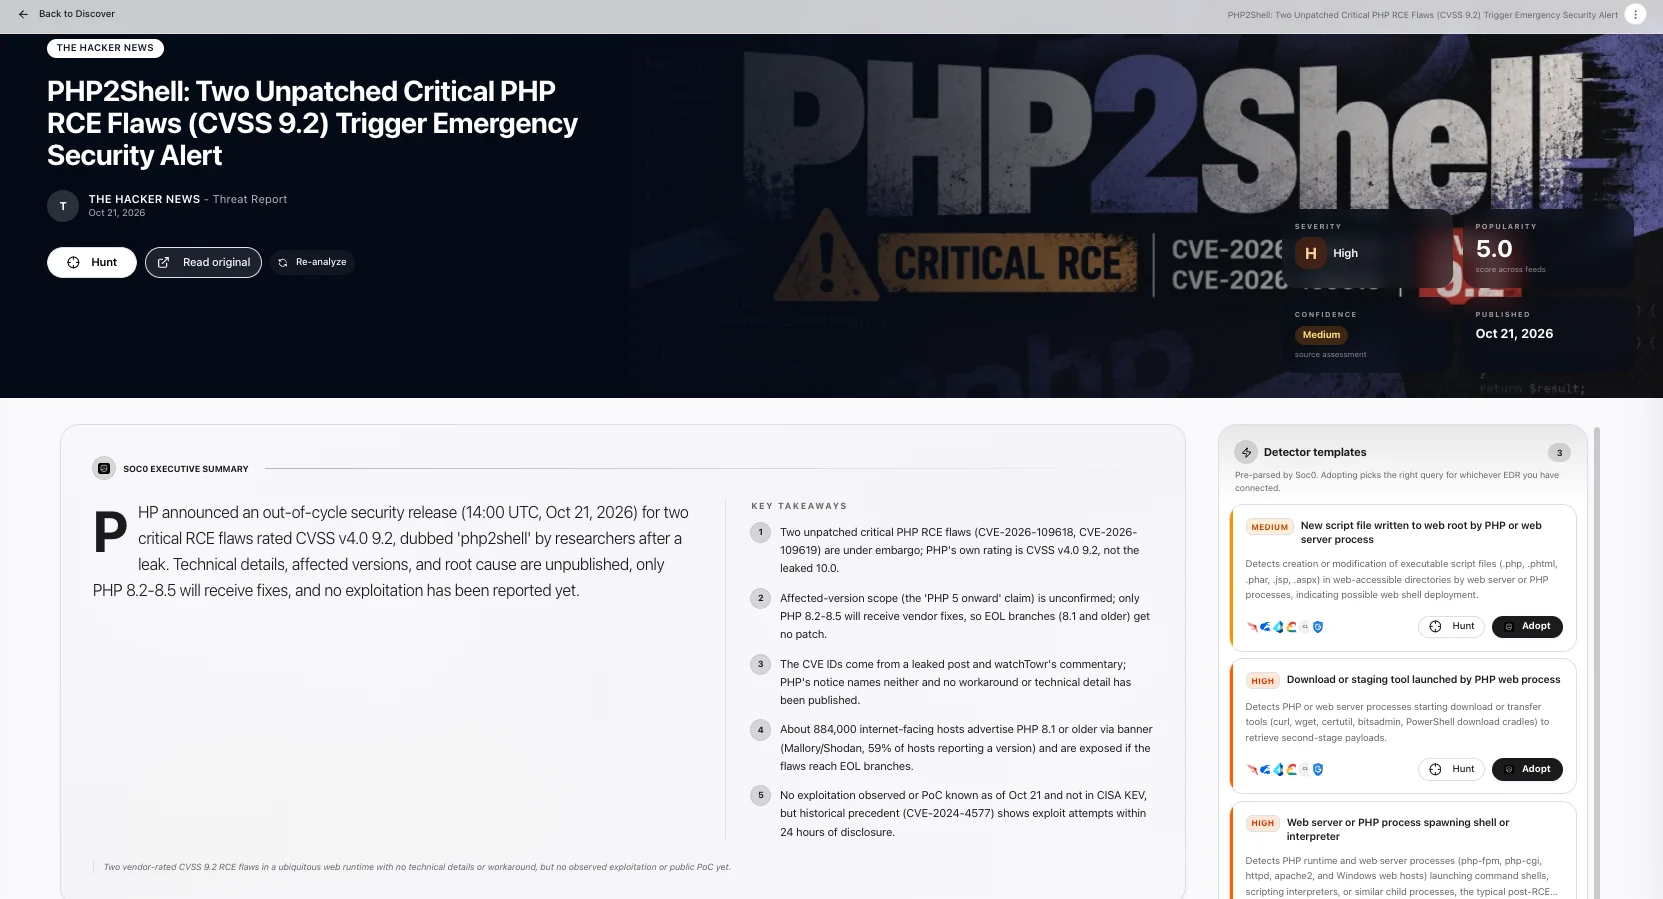
Detectors written, replayed on your history and shipped versioned. On fused network, identity, endpoint and cloud data.

01Write
Start from 5,000+ templates. Not zero.
- threat report
- Paste the article
- mitre att&ck
- Pick a technique, e.g. T1547.001
- plain language
- “Unsigned binaries in temp folders”
- output
- A detector for your connected sources
Want to try it now? Build a detector free in Detector Studio →
02Behavior
Catch what breaks the pattern.
- identity
- svc_backup signs in interactively
- endpoint
- bitsadmin.exe on host-eng-007.example
- network
- 2.1 GB to a rare ASN
- cloud
- Bucket read by an unused role
03Test, then ship
Prove it on your history.
- replay
- Run on stored history first
- tune
- See what it would have fired on
- release
- Versioned, with a change note
- rollback
- One step back
04Coverage
Know exactly what’s watched.

Every hit arrives with its story. Who investigates the hits →
Get started
Transform your security operations with Port0.
Thirty minutes. Your tools, your alerts, a live investigation.